Stop fake sign-ups, trap hacker bots, and catch hidden admin accounts — automatically.
Bot Assassin deletes bot accounts the moment they’re created, bans the IP of any bot that tries a hacker’s favourite usernames, refuses attempts to sneak admin rights onto an account, and finds admin accounts that malware hides from you. Every time it acts, you get an email.
Spam sign-ups pile up
Bots register fake accounts by the hundreds to post spam, test stolen passwords, or wait for a security hole.
Bots hammer your login
They try admin, wpadmin, wp_update and dozens more names, all day long.
Hacked sites get secret admins
One plugin security hole can turn a normal account into an administrator — and some malware hides it from your Users list.
Sign-up protection
Kills bot sign-ups instantly
When a new account is created with a role you’ve chosen, Bot Assassin deletes it on the spot, blocks its username and email so it can’t come back, and emails you the details. The visitor sees your own message instead of a welcome email.
- Pick exactly which roles to remove — Subscriber, Customer, or any custom role
- Your own message for blocked visitors, shown on the login screen
- Sign-up log of every email used to create an account, with one-click CSV download
- Blocked accounts list with one-click Unblock
- Accounts you add yourself as an administrator are left alone
- Catches accounts made through any sign-up form — WordPress, WooCommerce and others
Choose which roles to remove, write your blocked-visitor message and set up email alerts.
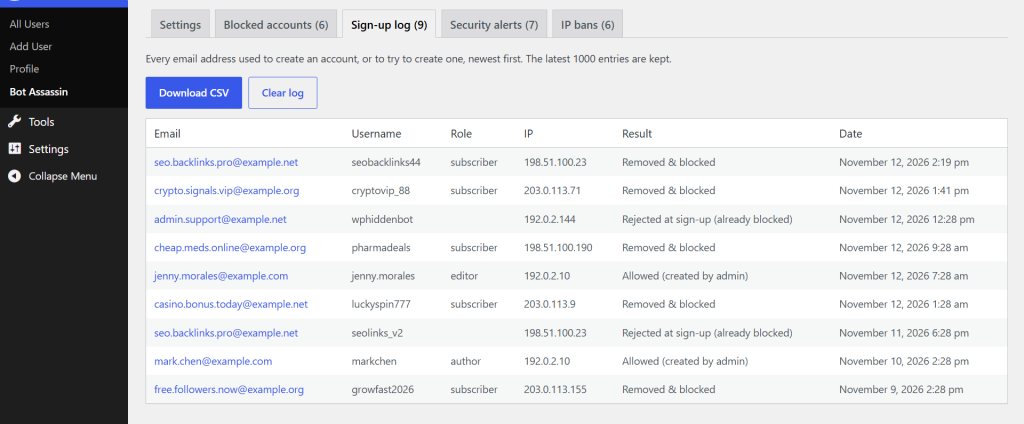
The sign-up log: every email used to create, or try to create, an account.
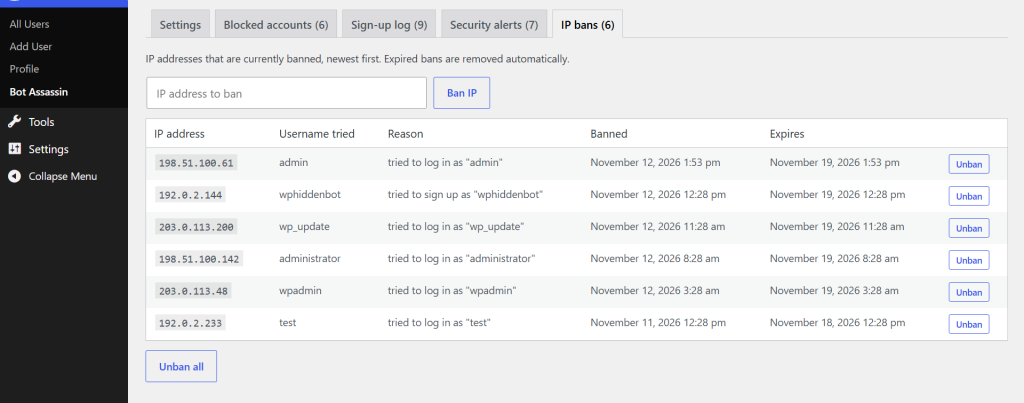
What a blocked visitor sees.
Username trap
Bots that try “admin” get banned
Bots try the same usernames on every WordPress site. Bot Assassin turns those names into a trap: anyone who tries to log in or sign up with one gets their IP address banned.
- Ready-made trap list:
admin,administrator,wpadmin,wp_update,wphiddenbotand more - Wildcards:
wp*admincatcheswpadmin,wp-admin,wp_superadmin… - Ban for 1 hour, 24 hours, 7 days, 30 days, or until you remove it
- Ban from the login pages only, or from your whole site
- Catches XML-RPC login attempts too
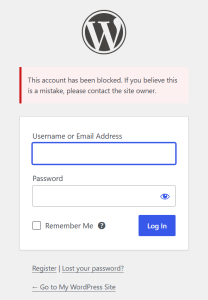
- See, add and remove bans from one screen
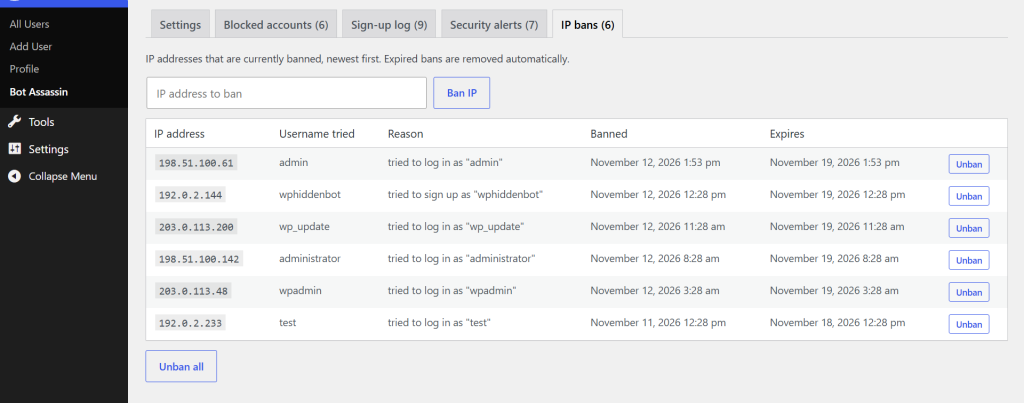
Every ban, the username that triggered it, and when it ends.
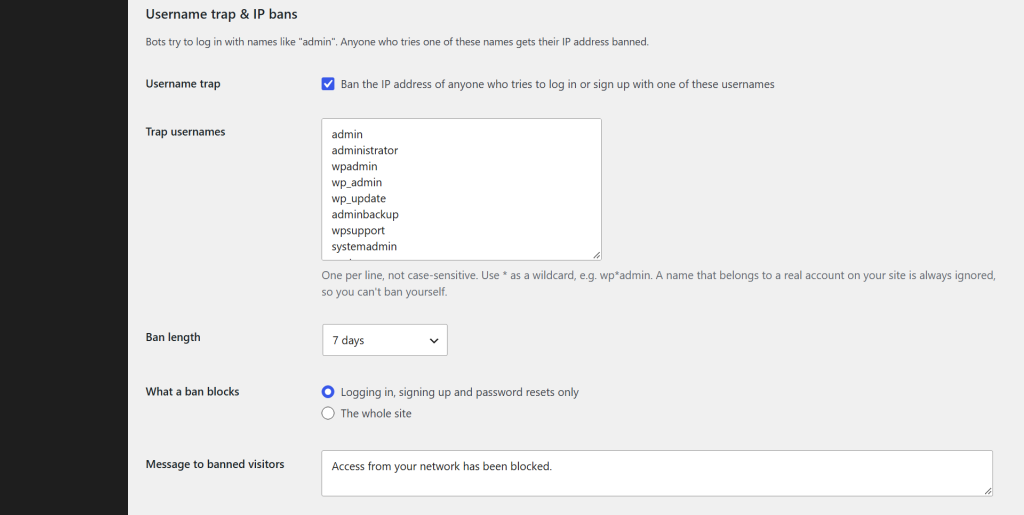
Edit your trap list, ban length and what a ban blocks.
Admin protection
Nobody becomes an admin unless an admin says so
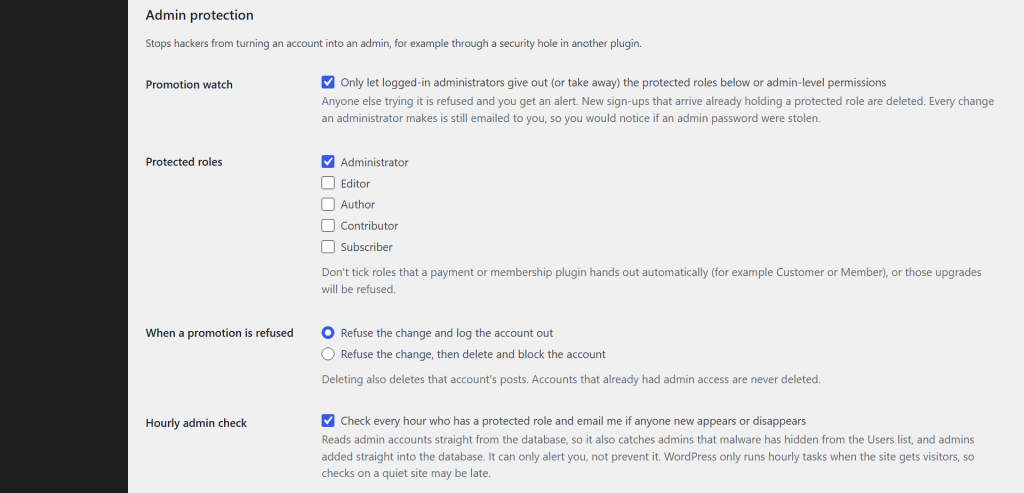
Most WordPress hacks end with the attacker becoming an administrator. Bot Assassin’s promotion watch only lets a logged-in administrator hand out admin rights.
- Anyone else trying it is refused, logged out and reported to you
- Optionally delete and block the account that tried it
- Also guards admin-level powers like installing plugins or editing users
- New sign-ups that arrive already holding the Administrator role are deleted
- Every admin change you make is emailed too — so you’d notice a stolen admin password
Hidden admin detection
Finds the admin accounts malware hides from you
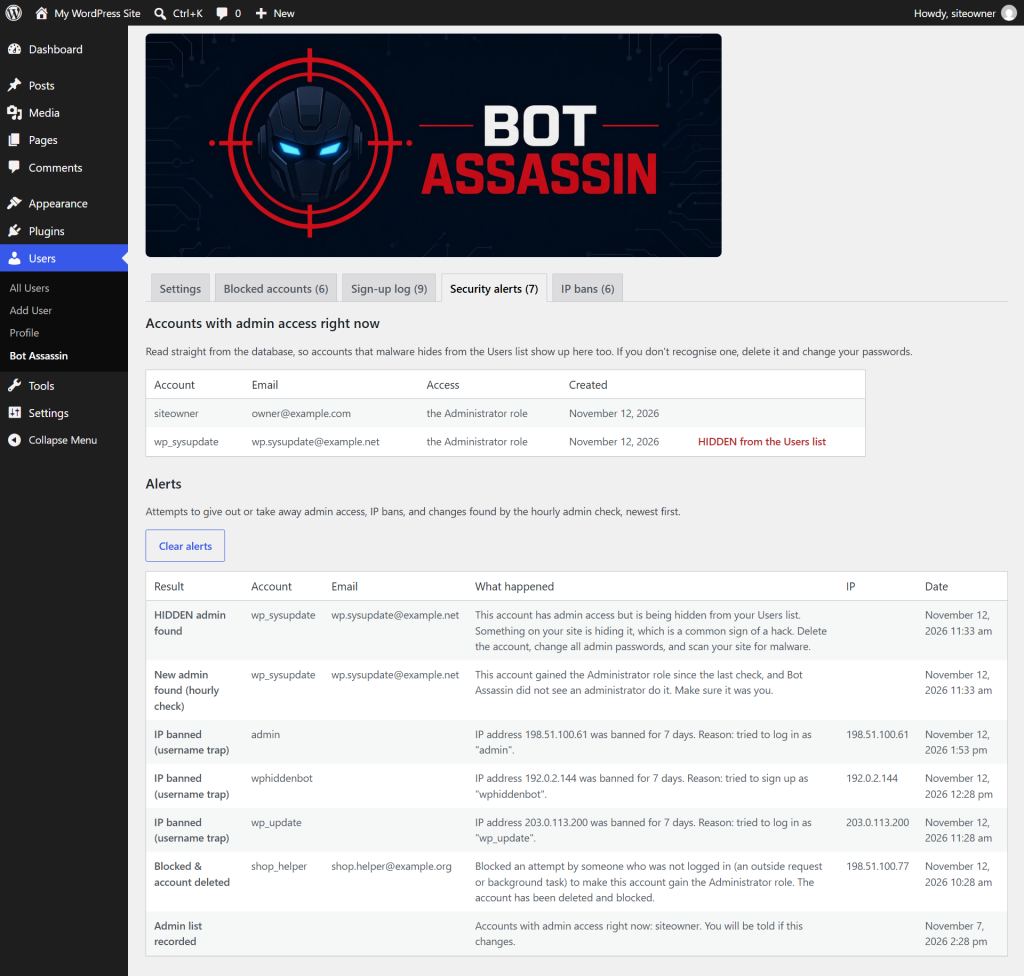
Every hour, Bot Assassin reads your admin accounts straight from the database. If an admin appears that no administrator created — or one is being hidden from your Users list — you’re alerted straight away.
- Live list of every account with admin access, with hidden accounts flagged in red
- The first check emails you your admin list, so an admin planted before you installed Bot Assassin still shows up
- Alerts when admin access disappears, too
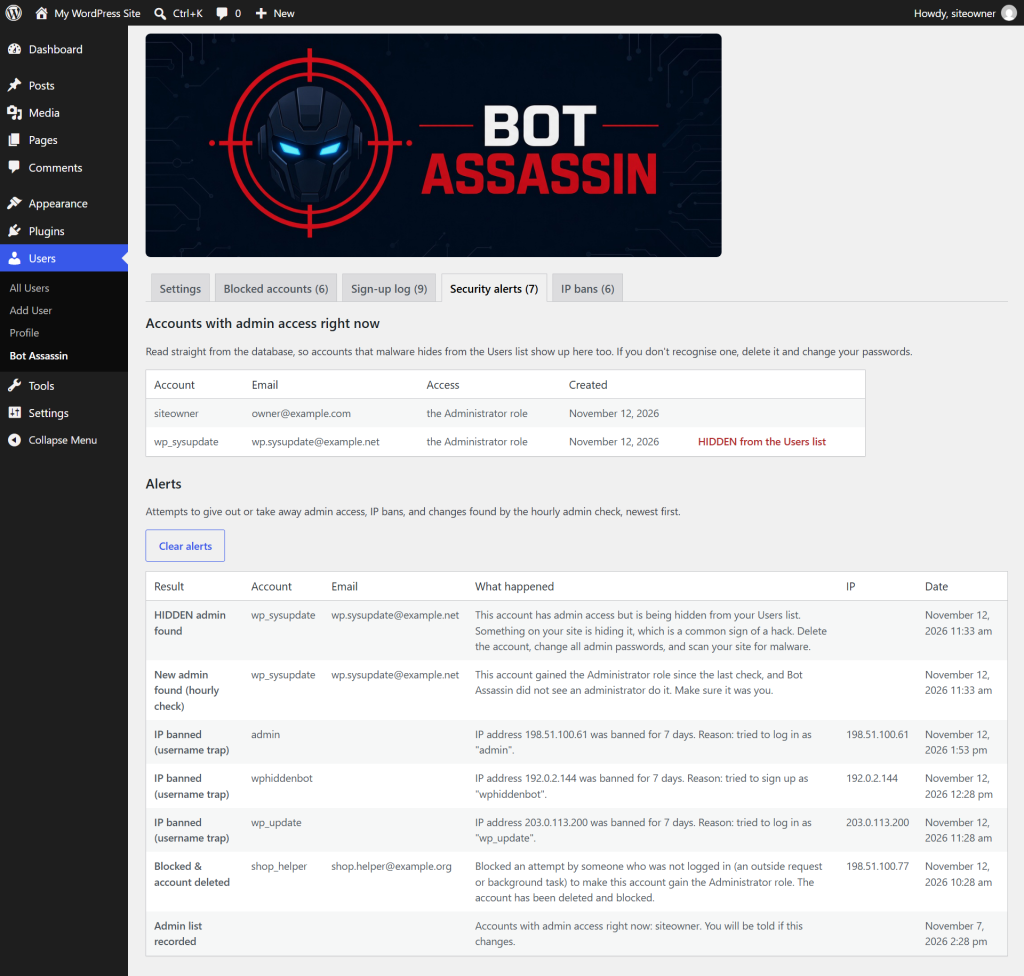
A hidden admin account caught, alongside banned bots and a blocked attempt to grab admin rights.
Built so you can’t lock yourself out
- Trap names that belong to a real account are always ignored
- IPs administrators recently used are never banned
- Your own “never ban” allowlist
- Private and local network addresses are never banned
- Works behind Cloudflare or a proxy with one setting
- Emergency off-switch: one line in
wp-config.php
Built secure
- Every admin action checks WordPress security tokens and administrator permissions
- Everything shown on screen is cleaned first
- CSV exports are protected against spreadsheet formula tricks
- Alert emails capped at 20 an hour, so a bot flood can’t bury your inbox
- No tracking — it only contacts shadowsplitter.com to check your license and fetch updates
- Uninstalling removes all of its settings and logs
Questions
Will it delete my real customers or members?
Only accounts with the roles you tick are removed, and WooCommerce’s Customer role is left unticked out of the box, so shoppers can still create accounts. If other real people need to sign up — members, for example — untick their role too. The username trap, IP bans, admin protection and hidden-admin check keep protecting you either way.
Can I lock myself out?
It’s designed not to: real usernames never trigger the trap, and IPs administrators have used are never banned. If it ever happens, one line in wp-config.php switches bans off.
Does it work with Cloudflare?
Yes — choose “Behind Cloudflare” in the settings so it reads each visitor’s real IP.
Will it slow my site down?
No. It only does real work when someone logs in, signs up, or an account’s role changes. The admin check runs in the background once an hour.
Does it stop password guessing on my real username?
The username trap bans bots that guess common admin names. It doesn’t limit repeated wrong passwords on a real username, so use a strong password — or a hardware security key — on every admin account.
Does it replace a firewall or malware scanner?
No — it works alongside them. Bot Assassin focuses on accounts: fake sign-ups, bot logins, stolen admin rights and hidden admins.
What are the requirements?
A Bot Assassin license key (each works on one live site; test and staging sites don’t use it up), WordPress 5.8 or newer (tested up to 7.1.4) and PHP 7.4 or newer (tested on PHP 8.3).
What happens if I uninstall it?
All of its settings, logs and bans are removed.